Security Risk Assessment: A Step-by-Step Guide for Businesses
CS
In today's digital age, businesses face a myriad of security threats that can compromise sensitive data and disrupt operations. Conducting a comprehensive security risk assessment is essential to safeguard your organization against these threats. This guide will walk you through the process step-by-step, ensuring you have a robust security framework in place.
Understanding Security Risk Assessment
A security risk assessment is a systematic process of identifying, analyzing, and evaluating risks to an organization's information systems. It helps businesses understand potential vulnerabilities and implement measures to protect against threats. This proactive approach is crucial in minimizing the impact of security breaches.
Step 1: Identify Assets
The first step in any security risk assessment is to identify all assets within your organization. These assets can include hardware, software, data, and personnel. Understanding what needs protection is the foundation of an effective risk management strategy.
- Hardware: Computers, servers, and networking devices.
- Software: Applications and operating systems.
- Data: Customer information, financial records, and proprietary data.
- Personnel: Employees with access to sensitive information.
Step 2: Identify Threats
Once assets are identified, the next step is to recognize potential threats. These can range from cyber-attacks and data breaches to natural disasters and human error. Understanding these threats helps in developing targeted security measures.
Assessing Vulnerabilities
After identifying threats, it's crucial to assess vulnerabilities that could be exploited. This involves evaluating existing security measures and identifying weaknesses. Common vulnerabilities include outdated software, weak passwords, and inadequate employee training.
Step 3: Evaluate Risks
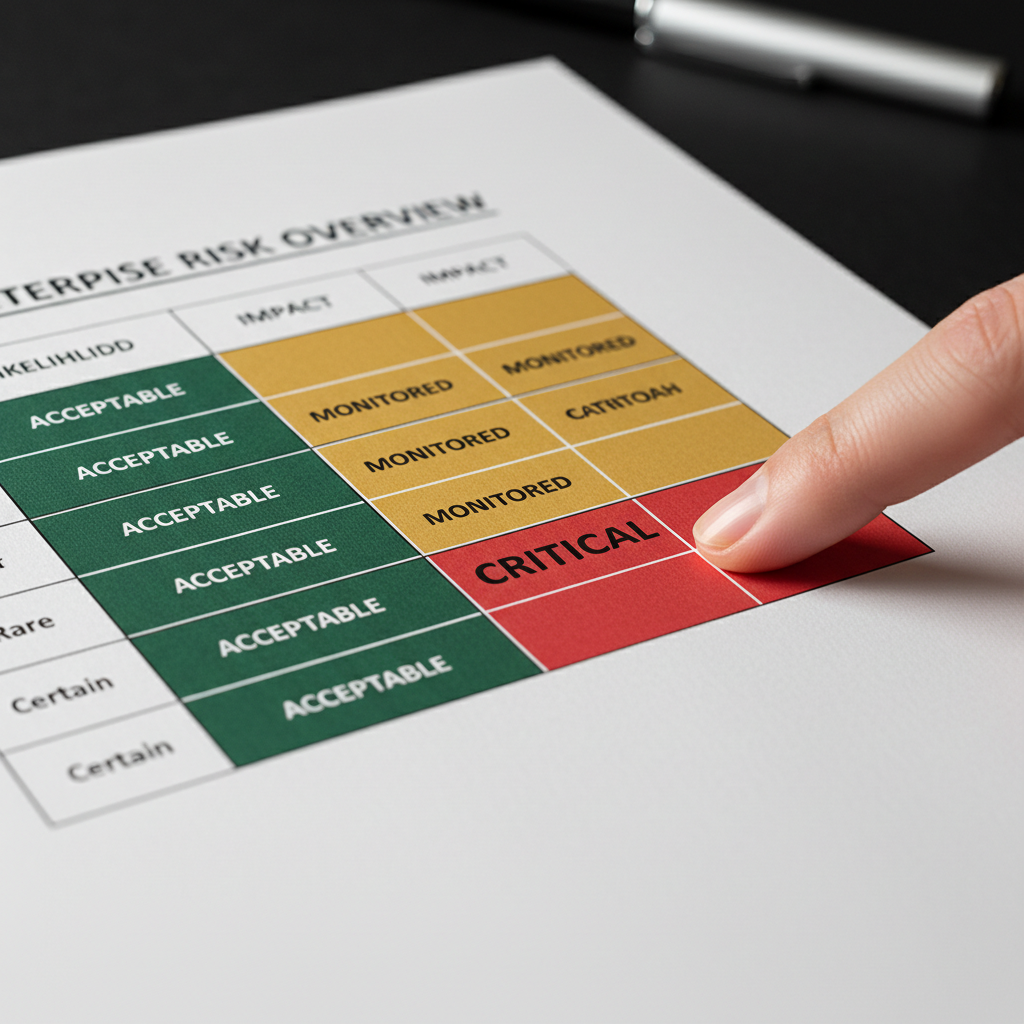
With an understanding of threats and vulnerabilities, the next step is to evaluate the risks. This involves determining the likelihood of a threat exploiting a vulnerability and the potential impact on the organization. This analysis helps prioritize risks and allocate resources effectively.
Step 4: Implement Security Controls
Based on the risk evaluation, implement appropriate security controls to mitigate identified risks. These controls can be preventive, detective, or corrective. Examples include firewalls, encryption, access controls, and incident response plans.
- Preventive Controls: Measures to stop security incidents before they occur.
- Detective Controls: Tools and techniques to detect incidents as they happen.
- Corrective Controls: Actions to restore systems and data after an incident.
Regular Review and Updates
Security risk assessment is not a one-time task. Regular reviews and updates are essential to adapt to new threats and changing business environments. Schedule periodic assessments and update security measures accordingly to maintain a robust security posture.
By following this step-by-step guide, businesses can effectively manage security risks and protect their valuable assets. Investing in a comprehensive security risk assessment not only safeguards data but also enhances trust with customers and partners.